
Cybersecurity
Incident Response Steps (NIST)
The NIST incident response life-cycle breaks incident response down into four main phases: Preparation; Detection and Analysis; Containment, Eradication, and Recovery; and Post-Event Activity.

The NIST incident response life-cycle breaks incident response down into four main phases: Preparation; Detection and Analysis; Containment, Eradication, and Recovery; and Post-Event Activity.
The blog post provides a short description of the ISO 27001 Annex A – controls.

NIST Cyber Security Framework (CSF) gives private sector organisations a framework of policies and controls to help prevent attacks from cyber criminals and detect and respond to ones that do gain access.
Overview The California Consumer Privacy Act (CCPA) was enacted in 2018 to give California consumers greater control over their personal information and to increase transparency
For any organization dedicated to security, commissioning a penetration test is a vital step. But navigating the quoting process can be surprisingly complex. A common
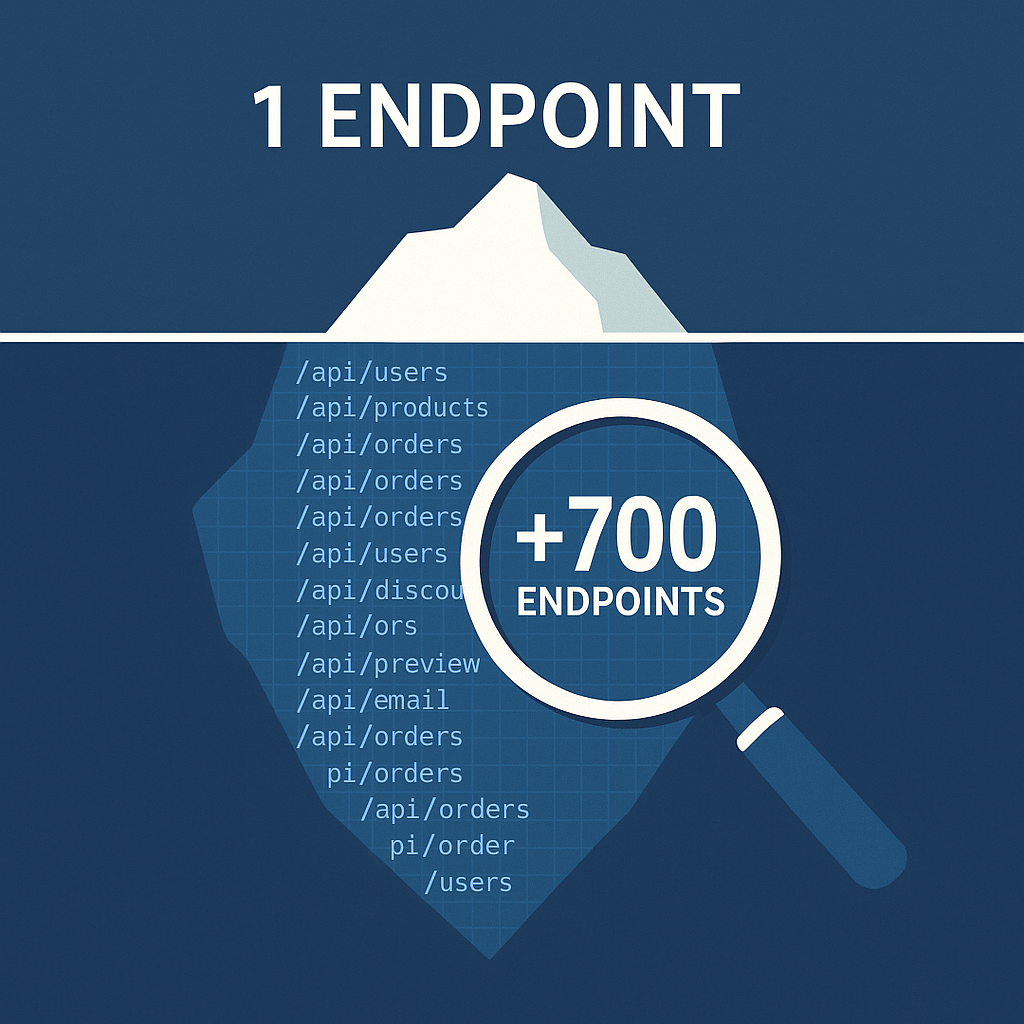
When a prospect approached us for a web‑application penetration test, the engagement looked routine: their statement of work listed just one API endpoint, the same
1. Why your /admin endpoint needs Zero‑Trust protection The Django admin console is a high‑value target: a single leaked credential can hand an attacker the keys to
Today, any SaaS or cloud vendor that wants to sell into Google (or Google’s customers) must clear a high bar. Google’s Vendor Security Assessment (VSA)